
Part 1 of 4 in our series for National Insider Threat Awareness Month
Today, Proofpoint is proud to sponsor the Insider Threat MatrixTM, an open, community-driven framework designed to help organisations better understand, detect, and investigate insider risk—both human and synthetic. Our support reflects a belief we have long held: the biggest challenge in insider risk is rarely a lack of tools. It is the absence of a common framework for describing risk, prioritising coverage, and connecting disparate signals into a defensible investigation. Insider Threat Matrix is governed independently by Forscie and stays vendor-neutral by design with sponsorships funding its development and infrastructure.
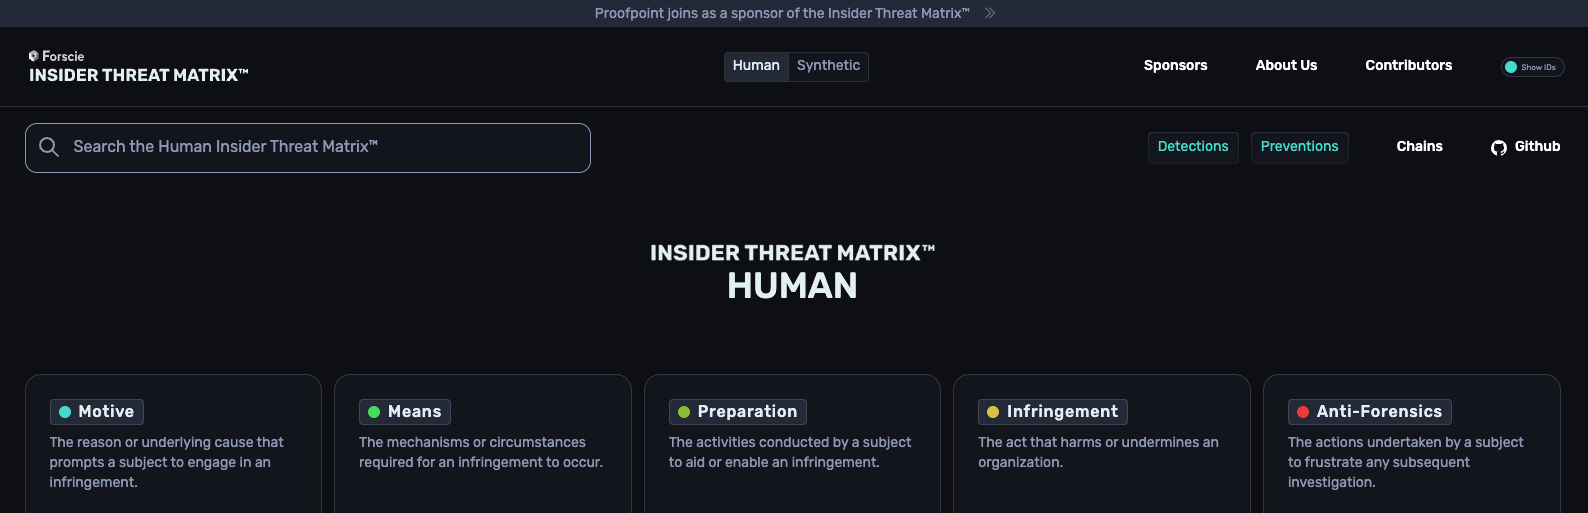
Developed by practitioners for practitioners, the Insider Threat Matrix provides that foundation. It maps the full lifecycle of an insider event across five categories: Motive, Means, Preparation, Infringement, and Anti-forensics, while documenting more than 800 techniques, motivations, and capabilities. Its breadth is both its greatest strength and the reason many organisations struggle to put it into practice.
The most successful teams do not treat the Insider Threat Matrix as a checklist to implement all at once. They use it to define common language across stakeholders (from white paper), prioritise use cases, assess visibility gaps and guide detection and prevention strategies. When approached this way, the Insider Threat Matrix becomes more than a framework. It becomes a practical roadmap for building a mature, measurable insider risk programme.
Why this Matrix Matters Now
Resolve the Fragmentation Problem
Insider risk has long endured a fragmentation problem. Security teams, HR, legal, compliance and insider risk practitioners often examine the same event through different lenses, using different terminology and measures of success. The result is confusion about what risks matter most, where coverage exists and how incidents should be investigated. The Insider Threat Matrix addresses this challenge by providing a common framework for understanding insider risk, creating alignment across stakeholders before a single alert is generated.
That alignment is what turns insider risk from a reactive security function into a strategic and proactive programme. Organisations that achieve the greatest success don't attempt to address every possible insider scenario at once. Instead, they use the framework to prioritise the risks that matter most to their business, whether that's intellectual property theft, source code exposure, misuse of privileged access, customer data loss or the risks associated with a departing employee. By focusing resources on the highest-impact scenarios first, teams demonstrate measurable outcomes, build credibility and create a roadmap for broader programme maturity.
Need Confidence in Visibility
The Insider Threat Matrix also helps organisations answer a fundamental question: Are we actually covered? Most enterprises already have significant investments in technologies such as network security, DLP, identity security, endpoint detection and SIEM platforms. Yet visibility gaps remain common, and understanding where coverage exists and where it does not is often difficult. By mapping priority use cases against the Insider Threat Matrix, organisations identify where they have meaningful visibility, where critical blind spots exist and where investments in people, process or technology will deliver the greatest return.
Address Proper Investigation Beyond Just Detection
Perhaps most importantly, the Insider Threat Matrix extends beyond detection. Many frameworks help organisations identify suspicious activity; far fewer help them understand and investigate it. The Insider Threat Matrix provides a structured way to connect behaviours, context and evidence across the lifecycle of an incident, giving investigators a more complete picture of what occurred and why. The result is an investigative approach that is more consistent, more defensible and better suited for collaboration with stakeholders across HR, legal, compliance and executive leadership.
The impact can be significant. Organisations that incorporate the Insider Threat Matrix into their insider risk programmes can reduce analyst workload, resolve cases faster and build greater confidence in their investigative outcomes. More importantly, teams gain a repeatable way to measure coverage, prioritise investments and continuously improve how they detect and respond to insider risk. One Proofpoint customer reduced the number of subjects requiring analyst review by 97% by mapping detections to the Insider Threat Matrix and correlating behaviour across 3–5 articles instead of triaging single infringements.
But understanding the problem is only the first step. Organisations still need the right capabilities to operationalise that understanding.
What a Successful Insider Risk Program Actually Needs
Sponsoring the Insider Threat Matrix reflects our commitment to advancing a shared industry framework and common language for insider risk. But a framework alone doesn't reduce risk. The Insider Threat Matrix helps organisations define insider risk scenarios. Across the enterprise programmes we see delivering measurable results, three core capabilities consistently differentiate mature, effective programmes from those overwhelmed by alerts and disconnected signals. Over the next three weeks, each of these insider risk pillars will be explored in this blog series:
Comprehensive Insider Visibility — Investigations are only as strong as the evidence behind them. Programmes should map native telemetry to the Insider Threat Matrix including communications sentiment, AI use, email, cloud and endpoint. The mapping delivers a complete evidence chain from day one.
Dynamic Protection — Reduce exposure without slowing the business. Protection should adapt to how employees actually work—factoring in access, role and risk—to safeguard data across every channel without blocking productivity.
Agentic Investigations — When telemetry spans the full insider threat lifecycle, investigations can run end to end: motive, preparation and infringement connected autonomously into an evidence-backed case. Analysts resolve faster and capacity scales without headcount.
Agentic investigations, dynamic protection—none of it works if you can’t see the behaviour. So, what does comprehensive visibility actually look like? That’s part 2.
Learn More