ACCOUNT TAKEOVER PREVENTION

Prevent Account Takeovers Across Cloud Accounts

Detect, investigate, and remediate account takeover (ATO) attacks in Microsoft 365 and other cloud environments before they escalate. 

Business professional using a smartphone while walking through a modern office.
Professionals working together in a busy modern office environment.

Rapid ATO Protection

Stop account takeovers before they spread

Detect and respond to unauthorized access in Microsoft 365, Google Workspace, and Okta with account takeover protection for cloud accounts. Identify compromised users, even when attackers bypass multifactor authentication (MFA), with behavioral analysis, threat intelligence, and automation. Investigate suspicious activity and remediate malicious changes before data loss or business disruption occurs.
Detect real account takeovers

Reduce false positives and focus on real threats with high-confidence detection.

Understand attacks quickly

See how attackers gained access and what they changed in a clear, complete timeline.

Respond and recover faster

Contain threats, revert changes, and restore accounts quickly with automated remediation.

Business professional working on a laptop beside an office window.

Threat Visibility Challenges

Account takeovers bypass traditional defenses

Account takeover attacks are common in cloud environments like Microsoft 365 and Google Workspace. While MFA helps, attackers regularly bypass it with adversary-in-the-middle phishing proxies, session token theft, and MFA fatigue attacks. Without clear visibility into account activity and automated response, attacks go undetected longer, increasing the risk of data breaches, lateral movement, and business disruption.

99 %
of organizations report attempted account takeovers

Proofpoint, 2025.

67 %
experienced a successful account takeover in 2025

Proofpoint, 2026.

59 %
of compromised accounts had MFA enabled

Proofpoint, 2026.

Product Capabilities

Detect and remediate account takeovers in real time

Proofpoint Account Takeover Protection detects and responds to compromised cloud accounts using threat intelligence, behavioral analytics, and machine learning. It correlates phishing, brute force, and other attack signals with cloud activity to identify compromises early. Security teams can quickly investigate activity, understand the attack sequence, and automate remediation to reduce risk and dwell time.

Features

Pre-Access Threat Correlation

Correlate phishing, brute force attacks, and login activity to see how attackers gain access and detect coordinated threats early.

Post-Compromise MFA Change Detection

Identify suspicious changes to MFA settings and authentication methods that indicate attacker activity in compromised accounts.

Attack Sequence Visualization

Track attackers' actions after they gain access, including changes to mailbox rules, file activity, MFA settings, and app access.

Targeted User Investigation

Prioritize incidents involving highly targeted users and accounts exposed to similar attack patterns.

Automated Account Remediation

Delete mailbox rules, revoke malicious apps, reverse attacker-controlled MFA changes, and remove malicious files automatically.

Cloud Account Activity Monitoring

Continuously analyze activity across Microsoft 365, Google Workspace, and Okta using API-based integrations for full visibility.

01 04

Why Proofpoint

Human-centric security vs. traditional security approaches

CapabilityTraditional Identity-Based SecurityProofpoint Account Takeover Protection
ATO detection Focuses on identity signals with limited detection after authentication Detects compromised cloud accounts, including attacks that bypass preventive controls, with AI and behavioral analytics
Attack context Provides individual detections that may require manual investigation to confirm account compromise Correlates phishing, brute force, and cloud activity automatically to reveal how attacks begin
Attack timeline Presents isolated events rather than a unified attack narrative Shows the full attack sequence from initial access through post-compromise activity
Post-compromise monitoring Monitors authentication events with less visibility into post-compromise attacker actions Detects mailbox rule changes, MFA manipulation, malicious apps, and file activity
High-risk prioritization Prioritizes individual alerts or risky events, requiring analysts to establish broader attack context Automatically prioritizes high-risk users and related attack patterns to speed investigations
Automated remediation Often relies on manual response across multiple tools Automatically revokes malicious access, reverses changes, and restores accounts quickly
Cloud coverage Provides visibility into individual identity controls without unified cloud activity monitoring Monitors Microsoft 365, Google Workspace, and Okta from one view
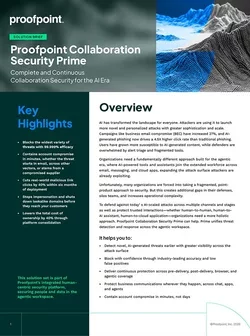
Proofpoint Collaboration Security Prime solution brief highlighting continuous collaboration security for the AI era.

Lock down fraud with Collaboration Security Prime

Stop the full range of attacks targeting your people, including threats, impersonation attempts, and supplier fraud. Proofpoint Collaboration Security Prime extends our human-centric security to messaging and collaboration tools, cloud apps, and the supply chain—all through one integrated platform.

Request a Demo

Detect and remediate cloud account takeovers faster with automated protection. Request a demo to see it in action.

Frequently Asked Questions

Common signs include unusual login locations, unexpected MFA prompts, and changes to mailbox rules. You may also see new app connections or suspicious email activity. These changes often indicate that an attacker has gained access and is trying to stay hidden.

Yes, attackers can bypass MFA using adversary-in-the-middle phishing proxies, credential stuffing, session token theft, and MFA fatigue attacks. These methods let them log in without triggering a second factor. This is why MFA alone cannot stop all account takeover attacks.

Detection relies on behavioral analysis, threat intelligence, and activity monitoring. Security tools look for unusual login attempts, risky sessions, and changes to account settings. These signals help identify compromised accounts, even when attackers use valid login credentials.

Attackers often change mailbox rules, modify MFA settings, or connect malicious apps. They may send phishing emails or access sensitive data. Without fast detection, they can stay active and expand their access.

Response includes removing attacker access and reversing malicious changes. Teams reset credentials, revoke sessions, remove harmful apps, and restore settings. Automated response helps contain the threat quickly and reduce impact.

Account Takeover Protection includes detection, investigation, and automated response. It monitors account activity, identifies suspicious behavior, and helps security teams act quickly. Advanced solutions correlate initial attack vectors such as phishing with cloud account activity to identify when a compromise has occurred.