AI Access Security

Secure Enterprise AI Adoption with AI Access Security

Discover and govern workforce AI use without slowing innovation. Apply runtime controls, protect sensitive data, and support compliance.

Two business professionals reviewing information on a tablet in a modern office, illustrating collaboration and secure AI access.

Secure AI Adoption

Empower your workforce to adopt AI safely

AI access security helps organizations discover, monitor, and govern how employees use generative AI tools, embedded AI features, and AI-connected applications. It inspects prompts, responses, uploads, and runtime behavior so security teams can reduce shadow AI risk, protect sensitive data, and maintain audit-ready records.

Accelerate AI adoption

Empower safe, scalable AI growth with unified governance that ensures visibility, control, and trust.

Reduce shadow AI risk

Find unsanctioned AI activity and bring risky usage into governed workflows.

Maintain audit-ready evidence

Record who used AI, what happened, what data was involved, and which policies applied.

01 04

The AI Governance Challenge

AI adoption is outpacing AI governance

Employees are using AI through approved tools, personal accounts, embedded SaaS features, and unsanctioned services. This creates hidden data flows, inconsistent policy enforcement, and limited evidence for investigations or regulatory review. Security teams need visibility and control at the point of AI interaction, not after sensitive data has already moved.

49 %

expect shadow AI incidents in the next year

50 %

expect data loss via AI tools in the next year

70 %

lack optimized AI governance

Product Capabilities

Govern AI with clarity, confidence, and control

Proofpoint AI Access Security lets you seamlessly scale your AI initiatives, with governance of every layer from day one. Security teams get the confidence to approve AI use, and leadership gets assurance that risk is managed as AI adoption expands. The same visibility, enforcement, and forensic capabilities extend to new AI tools, apps, and agents as you adopt them, growing your AI strategy without creating ungoverned exposure.

Features

AI Discovery and Inventory

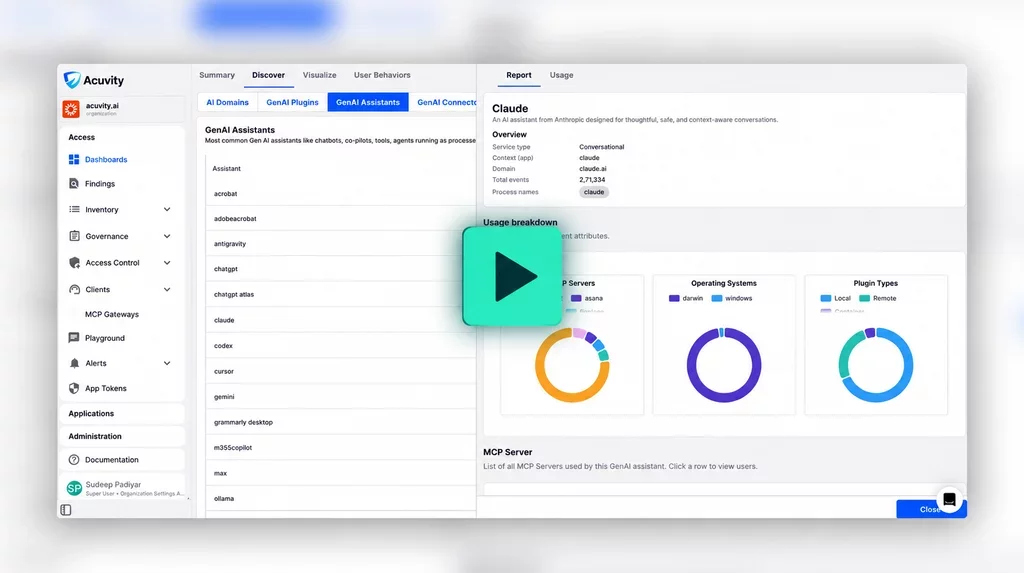
Discover and inventory all AI applications (first-party, third-party, embedded), AI agents (custom and managed), tools, integrations, external services, and MCP servers.

AI Runtime Observability

Get continuous runtime visibility into how AI systems behave when deployed, with behavior-level telemetry—not just prompt logs. Correlate activity across agents, tools, and MCP paths with multi-step execution context.

Runtime Inspection and Enforcement

Evaluate prompts, outputs, and model behavior at runtime against the intent of the task. Analyze text, image, and PDF content with 18 built-in detectors to separate legitimate activity from unusual or manipulated behavior.

Policy Enforcement

Enforce policy decisions at runtime across agents, tools, and MCP connections. Apply guardrails to block, redact, restrict, or escalate actions based on what’s happening in the moment, without rewriting applications.

Incident Response and SOC Integration

Route AI security events into your existing SIEM, SOAR, and SOC workflows for incident handling and governance escalation. Distinguish true security incidents from governance violations.

Forensics and Defensible Audit

Generate a forensic record of who initiated every AI interaction, what occurred, what data it used, and which policies and enforcement actions were applied. Full transaction reconstruction traces the entire user-to-outcome path, enriched with security context.

01 04

Why Proofpoint

Proofpoint AI Access Security vs. traditional cloud access controls

CapabilityTraditional Cloud Access ControlsProofpoint AI Access Security
AI usage visibilityOften identify access to known apps, but may miss embedded AI, local tools, and agent-mediated activityDiscovers sanctioned, unsanctioned, embedded, and agent-based AI activity
Runtime inspectionPrimarily control app access and sessions, not the contents or intent of AI interactionsInspects prompts, outputs, uploads, and context to identify risky or noncompliant activity
Data protectionMay require separate DLP and governance paths that are not tied to AI behaviorApplies data-aware policies to block, redact, restrict, coach, or escalate risky AI activity
Audit evidenceMay leave teams reconstructing evidence from fragmented logsCreates interaction records for AI use, policy decisions, and data involvement

Turn shadow AI into governed AI

Give your workforce room to innovate while keeping AI use visible, controlled, and defensible.

The definitive guide to shadow AI

Extend AI security beyond user access

Secure AI agents and the connections they rely on with complementary controls for agent behavior and MCP access.

01 04

Request a Demo

Discover and secure AI use across your workforce with AI Access Security. Request a demo to see it in action.

Frequently Asked Questions

AI access security helps organizations discover, monitor, and govern how employees use AI tools and AI-enabled applications. It goes beyond allowing or blocking access by inspecting AI interactions, applying policy at runtime, protecting sensitive data, and creating records for audit and investigation.

Enterprises can secure AI adoption by discovering sanctioned and unsanctioned AI use, monitoring runtime behavior, enforcing policy in real time, protecting sensitive data, and maintaining complete interaction records. These controls let teams expand AI use without relying only on app-level access decisions.

Security teams can detect shadow AI by continuously discovering AI tools, embedded AI features, agents, and connected services used across the organization. AI access security helps identify who is using AI, what data may be involved, and which activities need approval, restriction, or remediation.

Enterprise AI runtime security requires discovery, behavior-level observability, inspection of prompts and outputs, policy enforcement, SOC integration, and forensic audit trails. Together, these capabilities help teams evaluate what AI is doing during execution and respond when behavior conflicts with policy or intent.

Traditional cloud controls focus mainly on whether a user can access an application or session. AI governance also requires visibility into prompts, outputs, tool calls, data use, and multi-step behavior so teams can apply policy during the interaction, not only at login.