
Introducing User Risk Agents: Two AI Agents Built to Find and Protect Your Riskiest Users
At its annual Protect conference, Proofpoint® introduced User Risk Agents: two new agents built to identify the users who drive the most risk and protect them automatically.
Forward-Looking Statement: This blog contains information regarding anticipated product capabilities and roadmap plans. These statements reflect our current expectations and are subject to change. Future features, functionality, and timing are not commitments and may be modified, delayed, or canceled at Proofpoint’s discretion.
Proofpoint’s User Risk Agents are a new agentic approach to one of security’s most persistent problems: a small number of users in every organization account for a disproportionate share of organizational risk, and most tools still can’t tell you who they are, why, or how to mitigate that risk.
The scale of the problem is well documented. Sixty-two percent of security incidents involve the human element. Ninety-six percent of workers who took a risky action knew it was risky when they did it, which means this is a behavior gap, not just an awareness gap. If you plotted every user in your organization by how much risk they represent, the result would be a steeply descending curve. At the top would be a small percentage of users who carry an outsized share of the organization’s risk, and if one of them is compromised, the blast radius is severe.
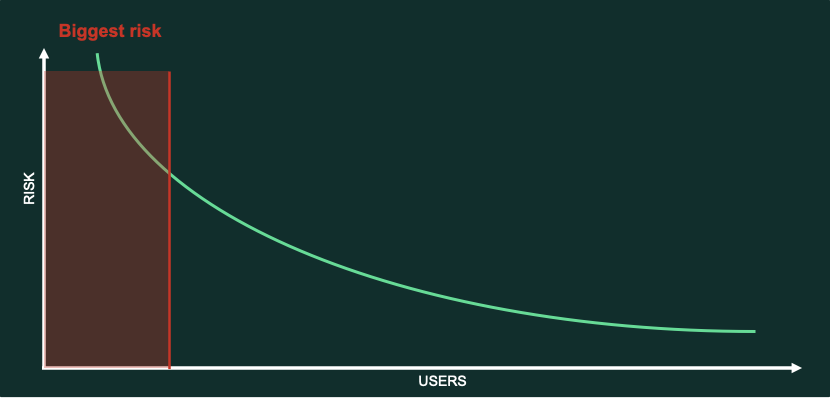
Fig. 1 A small percentage of users within an organization present the most impactful risk.
Where today's approaches fall short
Organizations have more visibility into human risk than ever before. Security awareness platforms educate users, and human risk management platforms aggregate risk signals from across the security ecosystem. Yet many security teams still struggle to translate that visibility into measurable risk reduction.
Security awareness training provides essential foundational knowledge and helps organizations meet compliance requirements. But by design, these programs are delivered broadly across the workforce, even though risk is rarely distributed evenly. In most organizations, a small percentage of users account for a disproportionately large share of the risk.
Human risk management platforms improve visibility by combining signals from email, endpoint, identity, and other security tools. But visibility alone doesn’t solve the problem. Security teams are still left to interpret risk scores, determine which users need attention, decide what intervention is appropriate, and manually coordinate a response across multiple systems.
The industry has gotten good at identifying human risk. What it still struggles to do is operationalize human risk reduction. That’s the gap our Red Team Agent and Blue Team Agent are designed to close. Rather than simply identifying elevated risk, they will continuously investigate, prioritize, and respond to it, creating a closed-loop system that helps organizations reduce human risk before it becomes an incident.
Two agents, one continuous loop
User Risk Agents close that gap with two purpose-built agents that will work together in a continuous loop of attack and defense.
Blue Team Agent will profile, protect, and coach your highest-risk users, transforming risk intelligence into personalized intervention and protection to harden each user’s risk posture, and is planned for general availability in Q1 2027.
Red Team Agent will continuously probe your organization the way an attacker would to find weak spots and vulnerable users. Based on that research, it synthesizes and orchestrates what it finds into a clear picture for your SOC team of where you’re exposed. It is planned to follow the Blue Team Agent release.
Together, they form a loop: Red Team Agent will surface where the organization is exposed, and Blue Team Agent will turn that into dynamic risk profiles, adaptive protection, and targeted coaching. Here’s a closer look at what was announced.
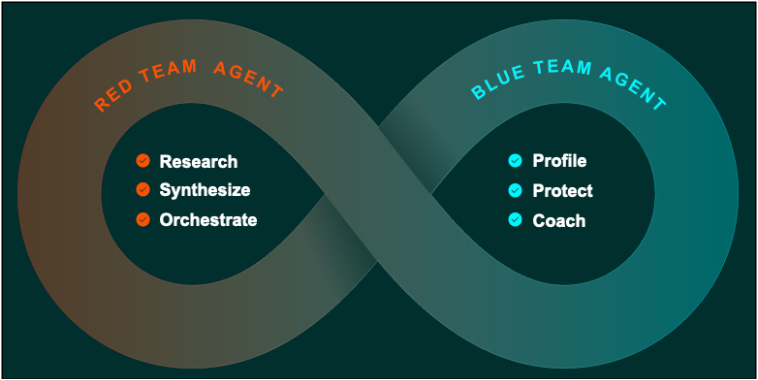
Fig. 2 User Risk Agents: two agents in a continuous loop to strengthen protection and reduce user risk
Blue Team Agent: Profile, Protect, Coach
Profile. Blue Team Agent will continuously analyze risk signals across threat exposure, security behavior, phishing resilience, sensitive data handling, AI usage, and business privileges. It will correlate native signals from across email, cloud, suppliers, data security, and AI, rather than relying on phishing simulation results alone or third-party scores. It’s designed to build high-risk groups unique to each organization automatically, explain why each group is high risk, and quantify the potential business impact if one is compromised, all without administrators manually defining risk criteria or segments. For example, a Finance VP’s risk isn’t driven by access alone. Blue Team Agent is designed to flag them as high risk because of broad access to payment systems combined with a pattern of risky behavior, such as repeatedly bypassing data handling controls, and threat exposure data showing they’re frequently targeted. Correlating those signals lets the SOC team see not just that the user is risky, but why, and what a compromise would likely cost the business.
Protect. Based on each group’s risk profile, Blue Team Agent will recommend and orchestrate adaptive responses, from targeted education and phishing simulations to real-time nudging, personalized threat briefings, and preventive controls like extended message inspection. Because these insights are shared across the Collaboration Security Platform, a rise in risk will trigger Proofpoint’s detection engine to apply deeper analysis automatically, without a manual policy update. For example, if a user in a high-risk group receives a suspicious message, that signal doesn’t just trigger extended inspection for that one message. The detection engine will identify who else in the organization received the same message and extend protection to them, turning one user’s risk signal into containment across the business.
Coach. Blue Team Agent is also designed to coach users directly, delivering guidance in the moment rather than through a static training calendar. For example, a user who clicks a risky link will get a real-time nudge explaining why the behavior is risky. And to support ongoing engagement, each user will receive an individual risk dossier showing what attacks are targeting them, what is driving their risk profile, and how their profile is changing over time.
What this means once available: SAT administrators will get an alternative to one-size-fits-all training, with interventions built around real risk rather than training completion alone. SOC analysts will get prioritized visibility into who is most likely to be compromised, richer context via the Proofpoint MCP server for SIEM and incident response workflows, and protection that adjusts on its own as risk changes, without maintaining separate policies across tools.
Red Team Agent: Research, Synthesize, Orchestrate
Red Team Agent will follow the release of the Blue Team Agent, and will round out the loop from the attacker’s side. Where Blue Team Agent defends, Red Team Agent is designed to continuously discover where the organization is actually exposed, probing the way a real attacker would rather than relying on point-in-time assessments.
One system is designed to serve two use cases: organization-wide red teaming that will test infrastructure and human risk exposure together, surfaced as a recommendation for the SOC analyst, and Red Team Agent-driven simulations designed to run as part of traditional security awareness training programs, spanning email phishing and smishing today, with vishing, deepfakes, and cross-channel scenarios planned. What Red Team Agent learns will feed directly into Blue Team Agent’s risk profiles and recommendations, rather than sitting in a separate report.
Focusing protection where it matters most
User Risk Agents will build on the foundation established by traditional security awareness programs with a more targeted, proactive approach. These agents are designed to continuously identify the small percentage of users who represent the greatest risk and engage them with personalized interventions before risky behavior leads to an incident. Where security awareness training establishes a baseline, User Risk Agents will focus additional protection, coaching, and risk mitigation on the users who need it most.
What’s next
Blue Team Agent is planned for general availability in Q1 2027, with Red Team Agent planned to follow. We’ll have more to share as both move toward launch, including deeper looks at how the two agents will work together in practice, and details on packaging and licensing as they’re finalized.
Blue Team Agent and Red Team Agent are built and designed to work as one system. Talk to your Proofpoint account team about what that looks like in your environment.