
Proofpoint’s business email compromise, lateral phishing, and supply chain threats, surfaced directly inside the Microsoft Defender portal.
One Console, Deeper Coverage
Microsoft 365 is the primary place enterprises now do business, and Microsoft Defender already brings a layered defense to it: native detection that scales across the whole ecosystem, backed by automated investigation and response. Business email compromise, lateral phishing, and supply chain threats are engineered to blend in with everyday business communication. Many organizations choose to complement Microsoft Defender with additional detections as part of a layered security strategy, giving their teams multiple perspectives on the threats most relevant to their business.
Today, we're extending our integrations with Microsoft to meet that need. Proofpoint is now part of the Microsoft Defender for Office 365 ICES Vendor Ecosystem, offering the choice to our customers to integrate Proofpoint verdicts into the Microsoft Defender portal and quarantine workflows already being run by security teams.
Better Together, By Design
Microsoft built the Integrated Cloud Email Security (ICES) Vendor Ecosystem to support exactly this kind of layered defense: an approved framework that lets specialized vendors extend native Microsoft Defender protections while keeping everything inside one unified experience. Proofpoint plugs into that framework directly, adding threat intelligence purpose-built for human-targeted attacks alongside Microsoft's platform-level defenses.
Microsoft Defender already provides strong native protection. Proofpoint Core Email Protection layers human-centric detection on top of that foundation, and its verdicts show up in the Defender console, so there’s nothing extra for analyst to open.
How It Works
When Proofpoint identifies a threat after delivery, it passes a verdict, confidence level, and threat details on that message to Defender through a Microsoft Graph API. Microsoft Defender determines the highest-severity verdict on the message, using the same precedence logic it applies across every detection source, from malware down through spam, and applies its standard post-delivery remediation automatically. It's the same action Microsoft Defender takes for its own native detections, so quarantine and remediation stay consistent no matter which layer caught the threat.
Here’s what that looks like in practice, from both sides of the inbox.
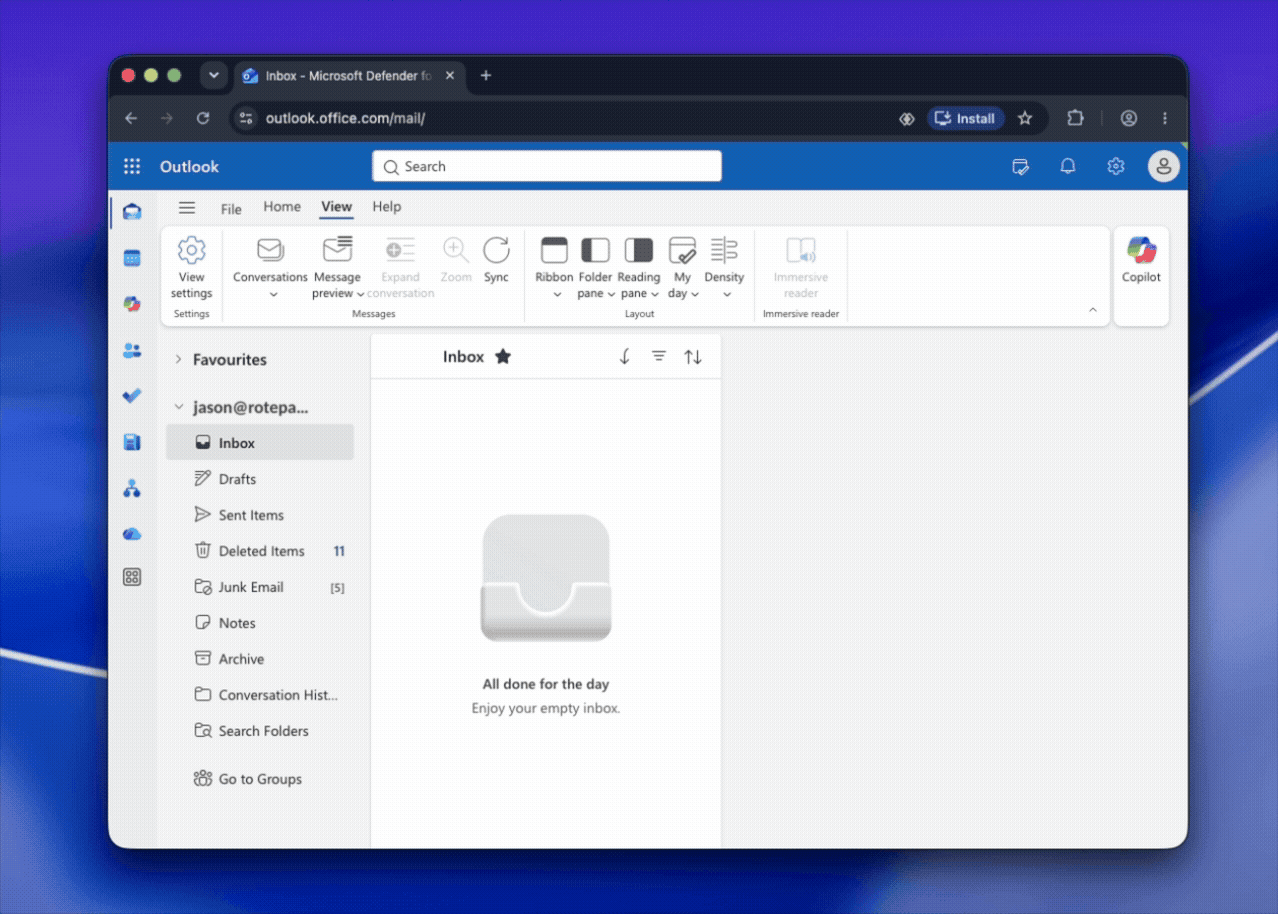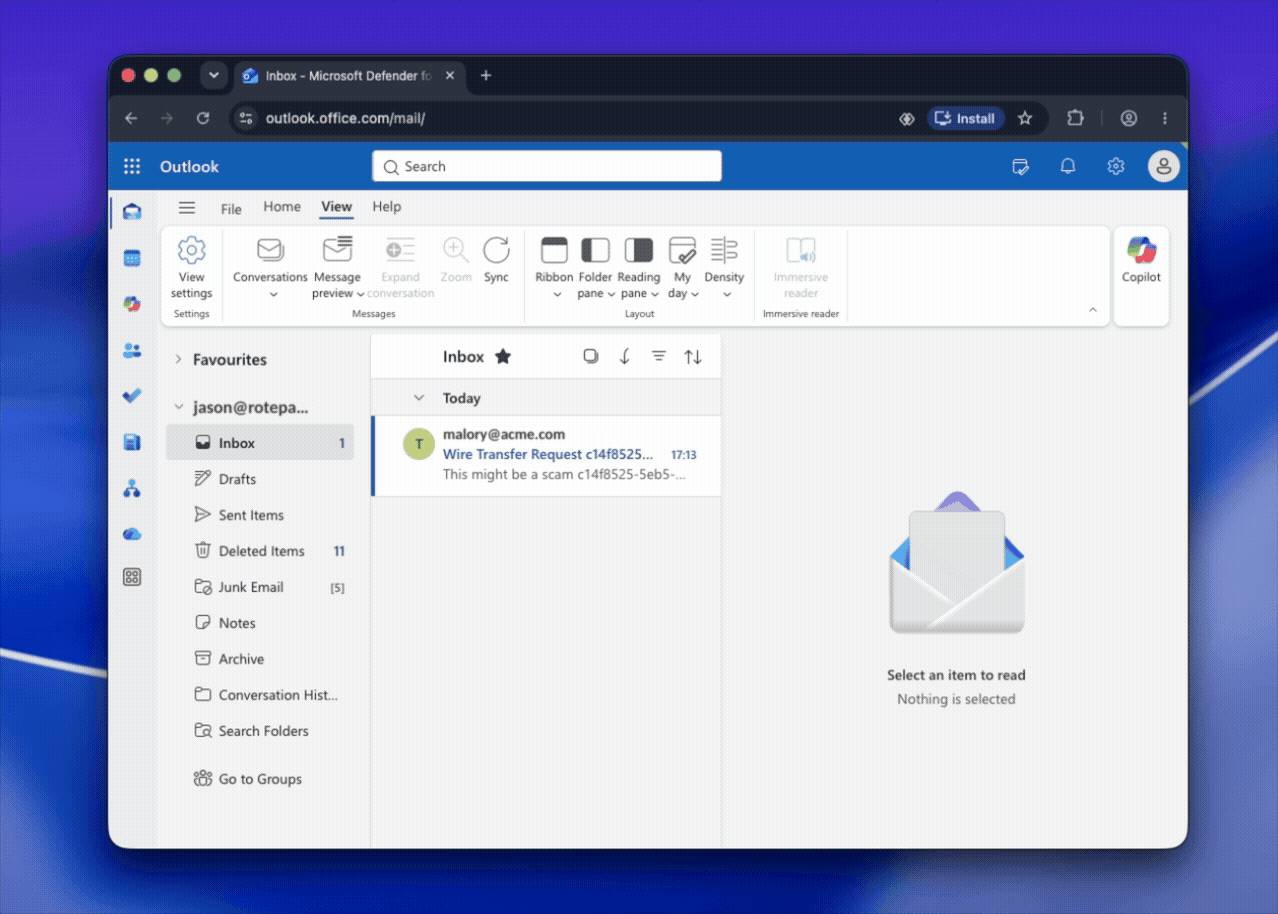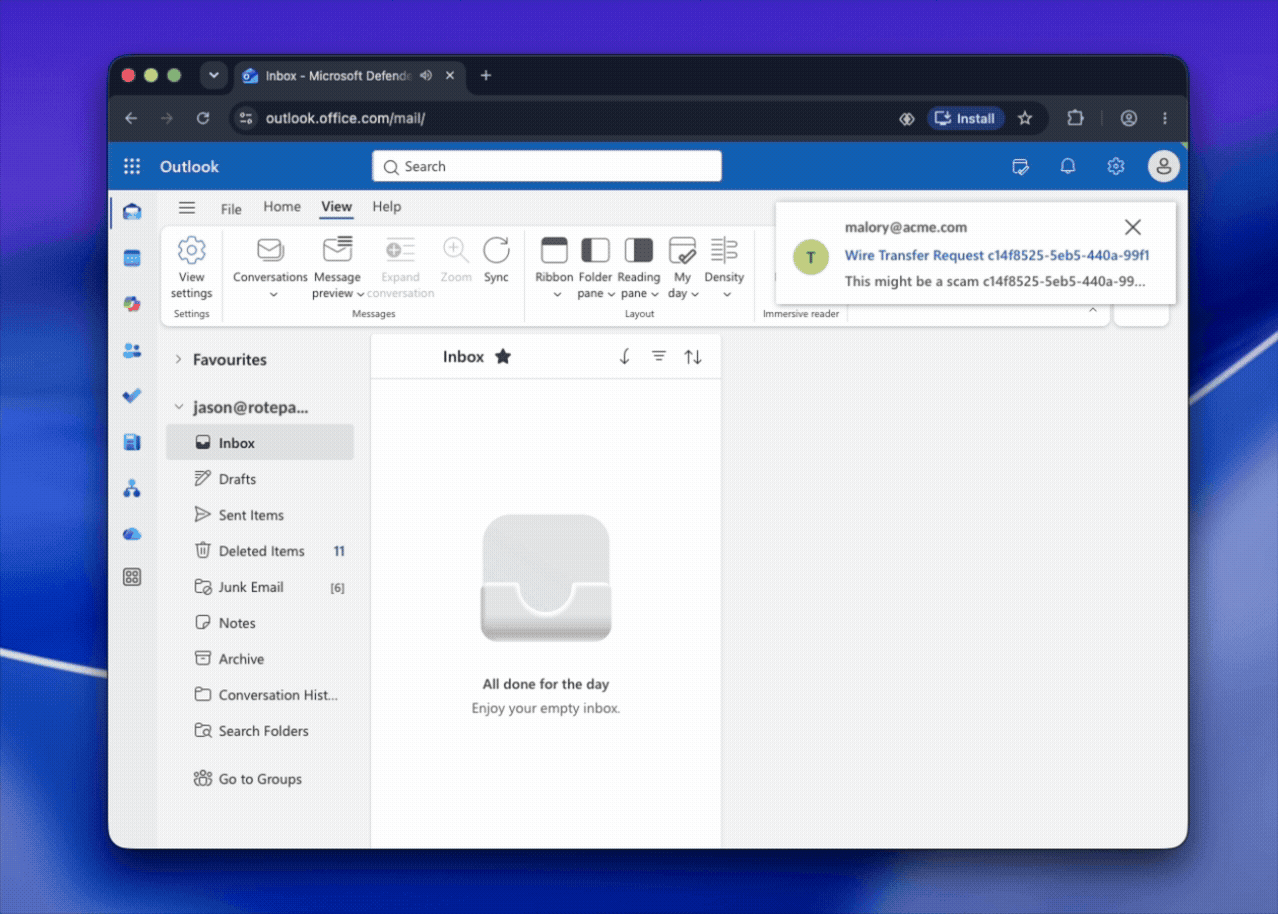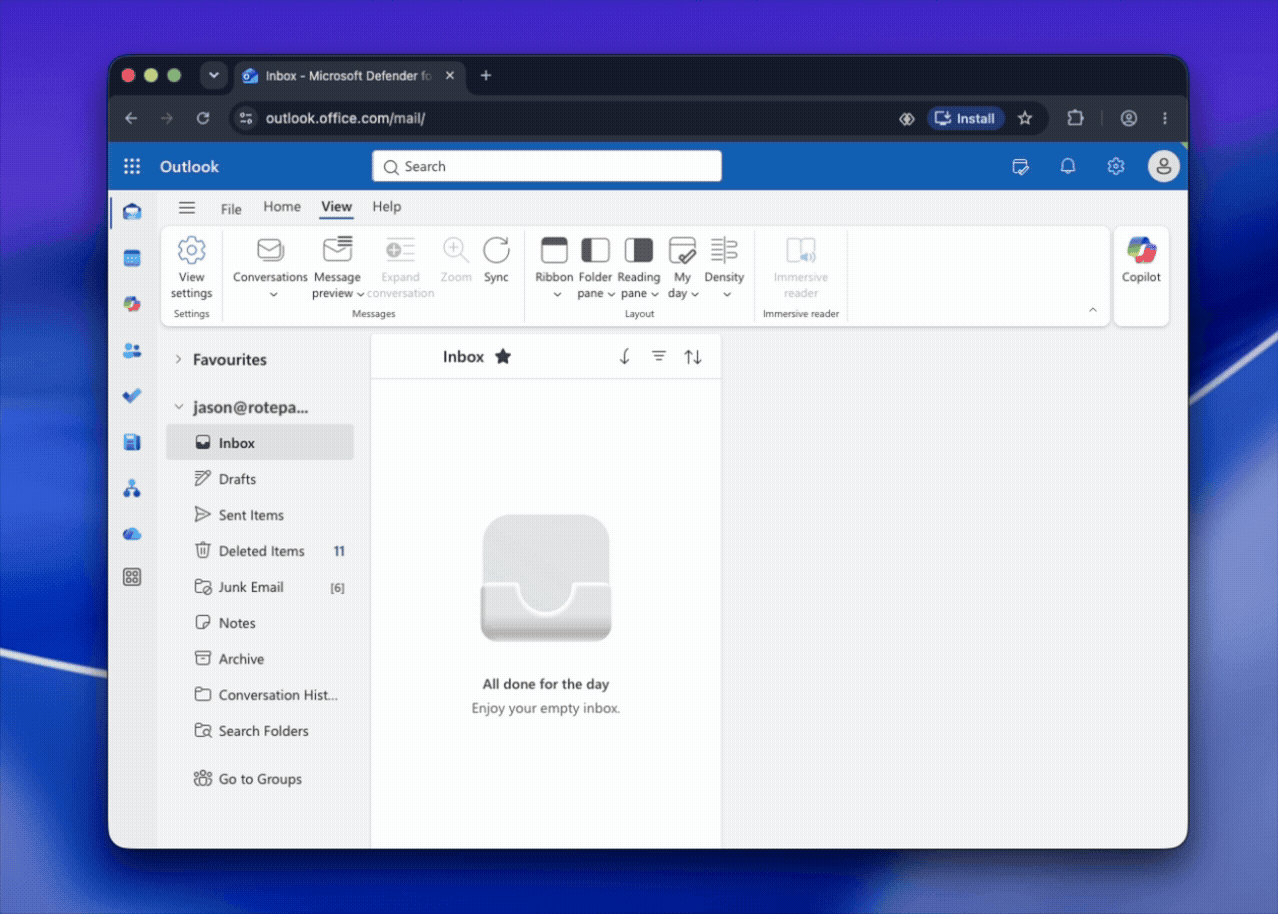
In the inbox:
A malicious email lands, Proofpoint flags it, and it’s pulled from the inbox while an alert notifies the user.
In the Defender portal:
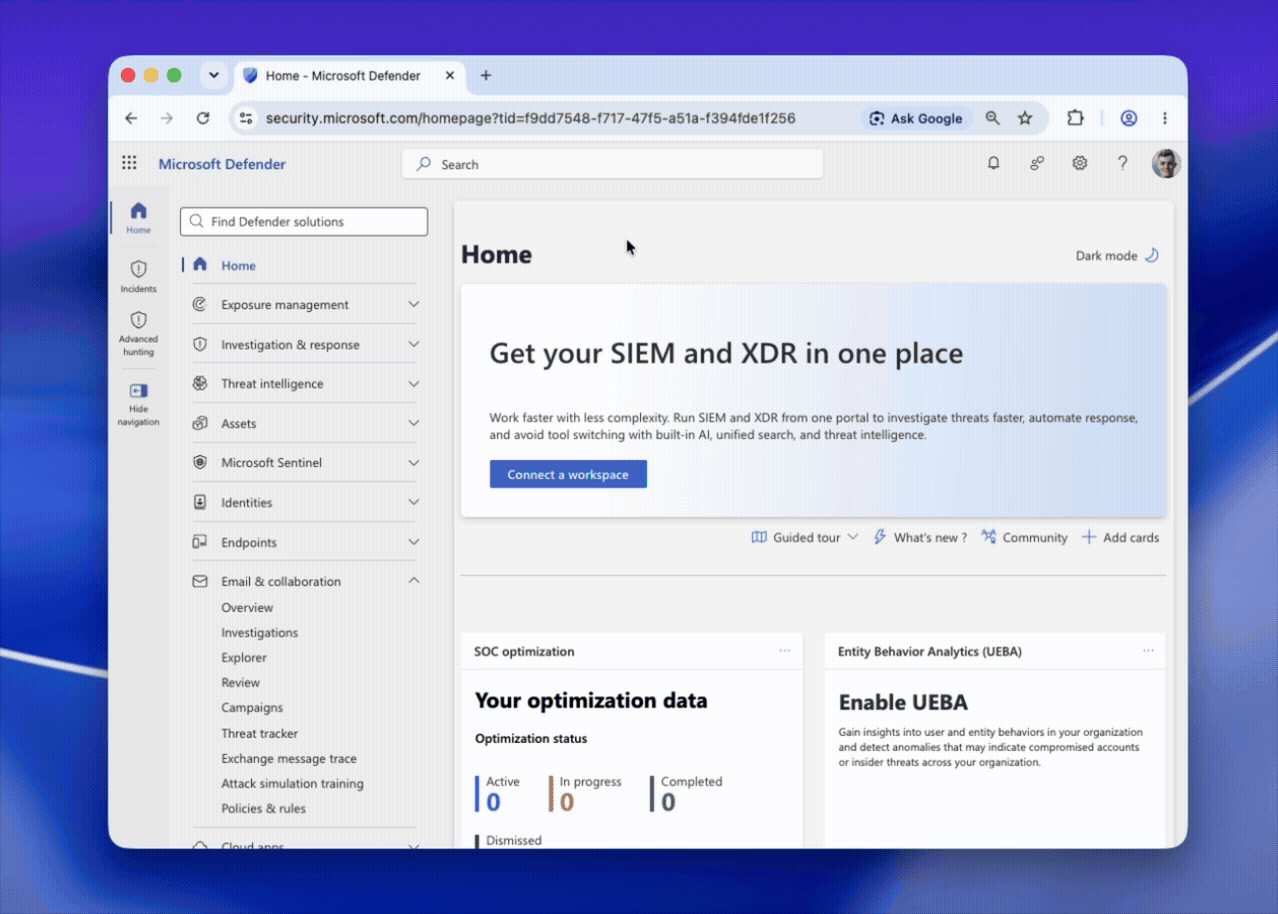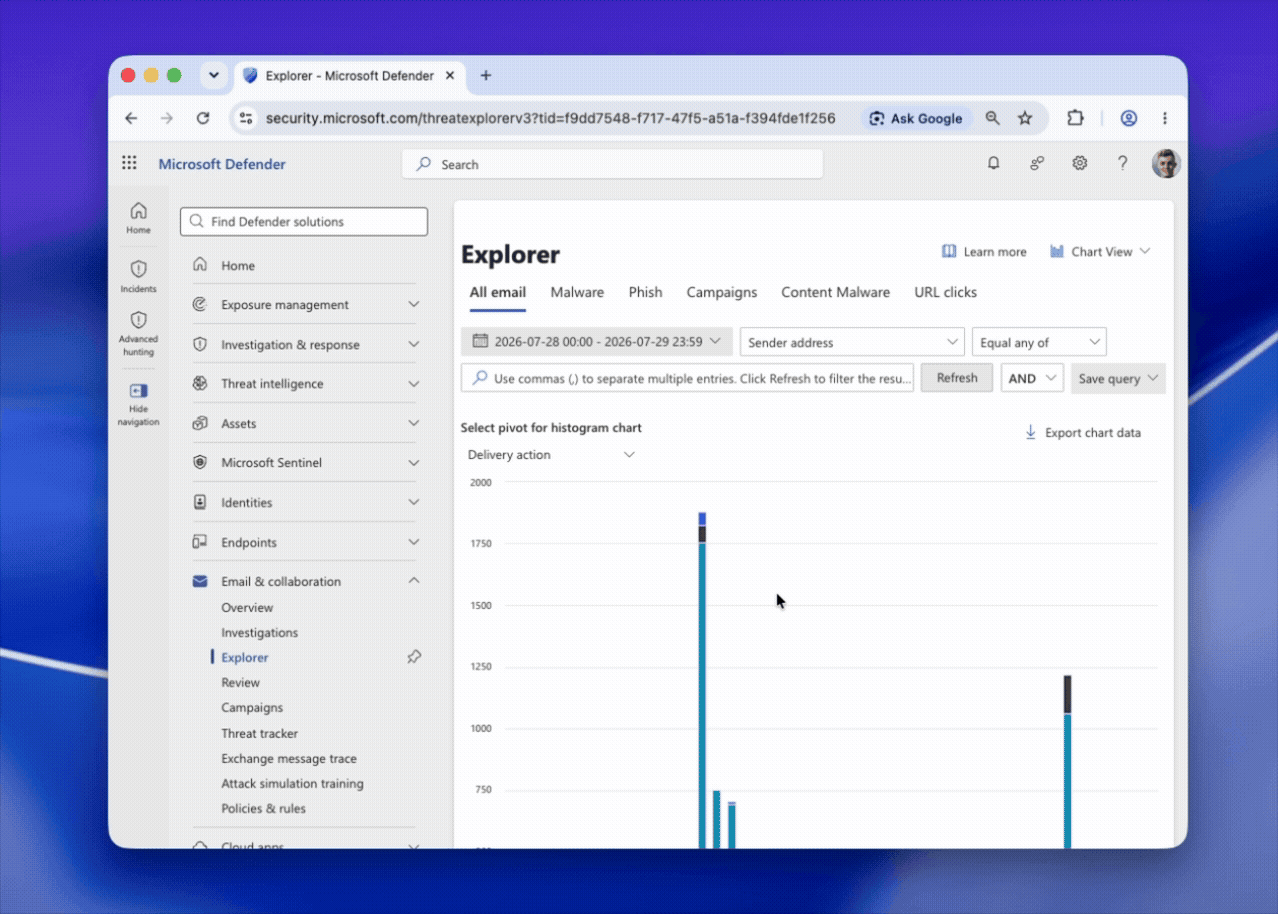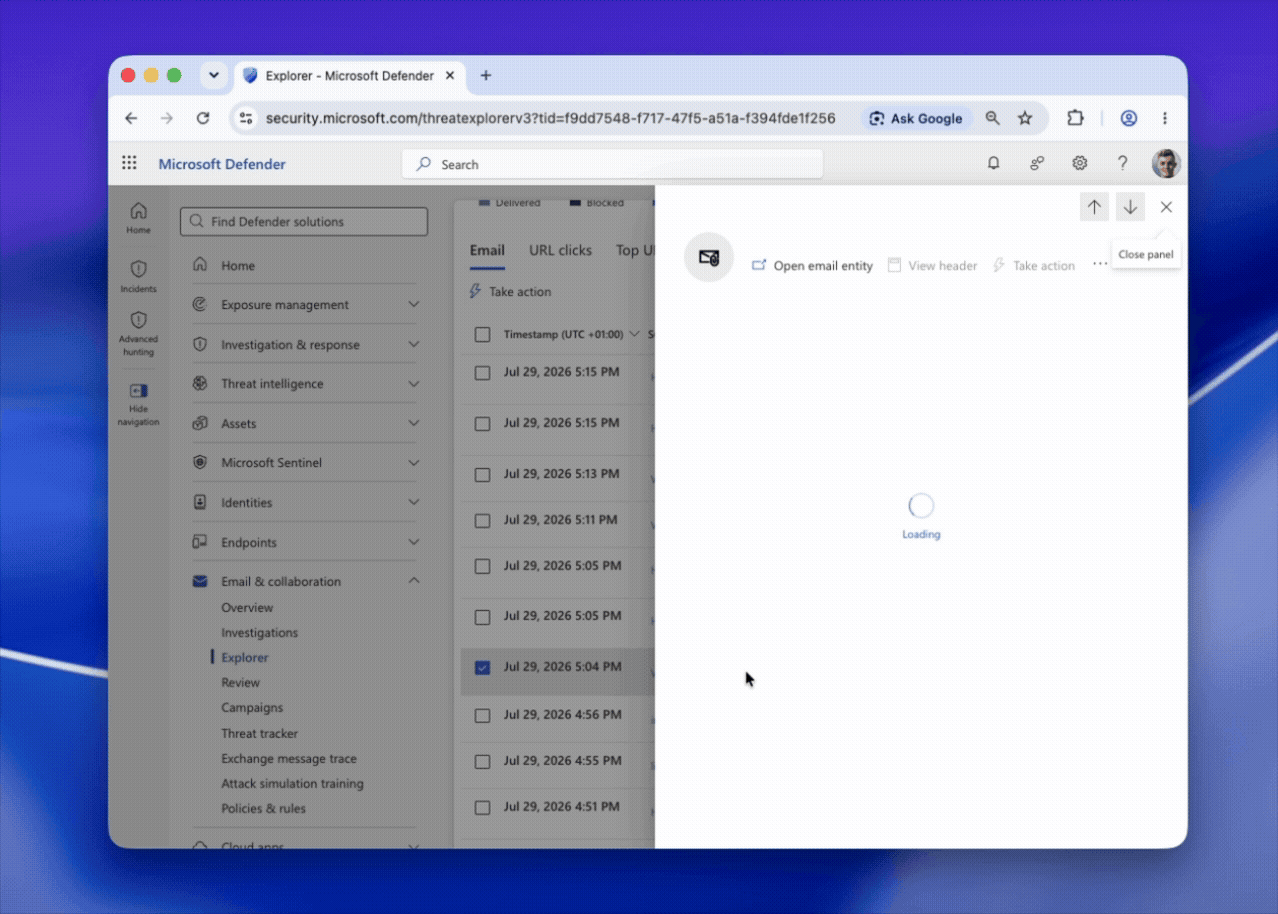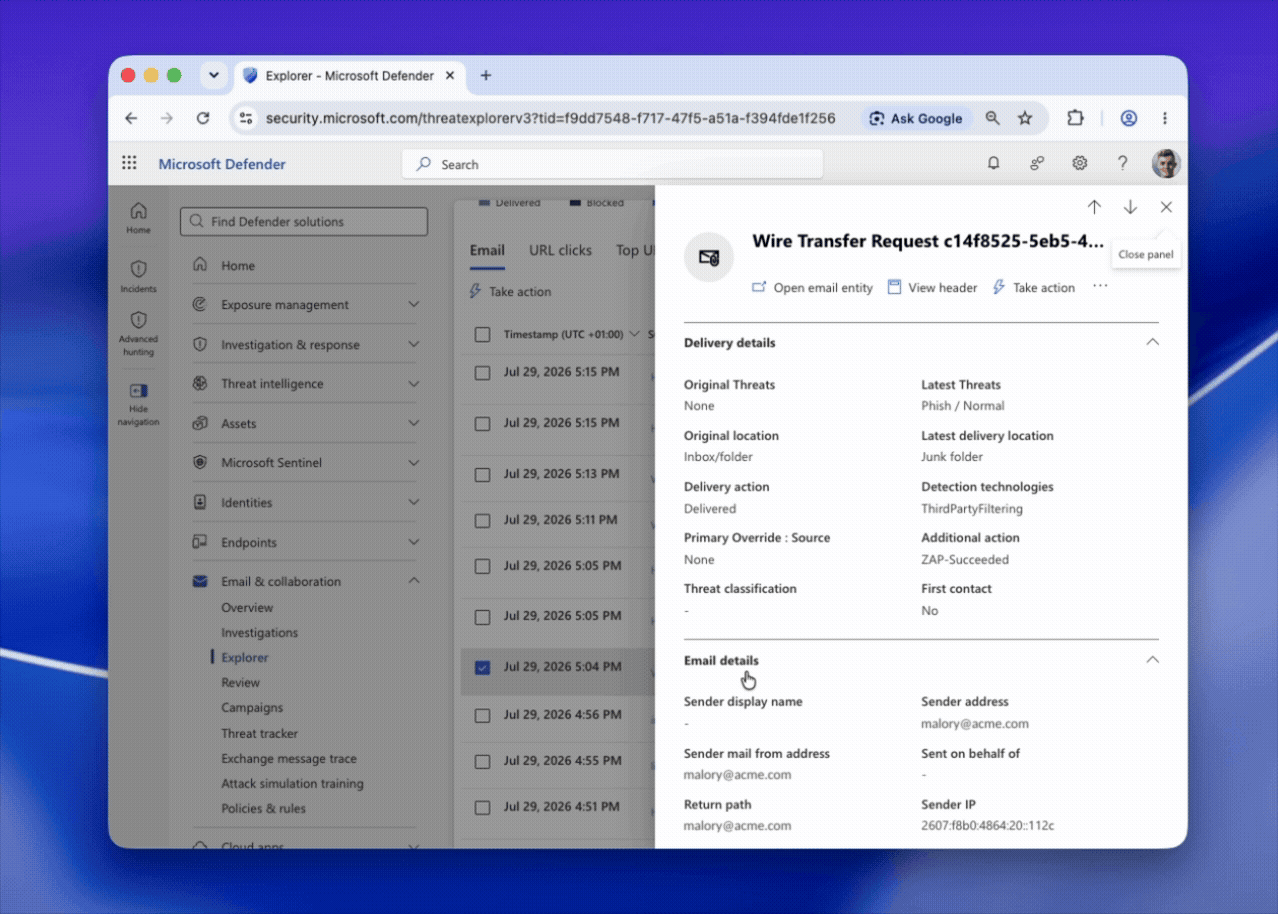
The Proofpoint verdict appears in the Defender for Office 365 dashboard, right alongside native detections.
Beyond Quarantine: The Full Investigation Picture
The integration goes well beyond quarantine. Once Proofpoint's verdicts are flowing into Defender, they show up across every unified experience Microsoft's ICES Vendor Ecosystem supports:
- Unified quarantine: search, preview, release, report, and remediate Proofpoint-flagged messages using the exact same workflow as native Defender detections.
- Threat Explorer: investigate Proofpoint-sourced detections in real time, trace delivery paths, and correlate signals alongside native threats.
- The Email entity page: see headers, delivery events, detection verdicts, and user actions for a flagged message in one place, including Proofpoint's vendor-specific detection detail, for a complete forensic view in a single pane of glass.
- Advanced Hunting: query Proofpoint-sourced detections alongside native ones using the same EmailEvents and EmailPostDeliveryEvents tables and KQL you already use, with extended schema support for Proofpoint-specific threat attributes.
- Reporting: Microsoft's own reports include an Efficacy metric that quantifies the unique detection value Proofpoint adds on top of native Defender coverage, a built-in way to see the return on the integration rather than take it on faith.
What's Next
As this integration matures, we will explore additional features and integration points based on joint customer requests.
Get Started
The integration is available to customers with Microsoft Defender for Office 365 Plan 2 or Microsoft 365 E5 licenses who are running Proofpoint Core Email Protection deployed via API (included in Collaboration Security Tier 2, Tier 3, and Prime). Confirm your eligibility, then turn on the integration in your Proofpoint console and complete Microsoft's permissions consent flow.
Verdicts start flowing automatically, at no additional cost, with no mail rerouting and no new infrastructure to deploy.
Learn more at proofpoint.com/us/solutions/secure-microsoft-365
Frequently Asked Questions
1. Does this replace Defender for Office 365's native protection?
No. Defender's native detection keeps doing exactly what it does today. Proofpoint adds a dedicated, human-centric layer alongside it. That layer gives BEC, lateral phishing, and supply chain compromise a second, behavioral lens, and adds detection value across spam, graymail, malware, and phishing.
2. Is there a cost for the integration?
No. The integration and Graph API support are included as part of your eligible Proofpoint and Defender for Office 365 licensing, at no additional charge.
3. What data does Proofpoint share with Microsoft?
A verdict, confidence level, and threat details on a specific message, passed via Microsoft Graph API. Defender uses that information to determine the highest-severity verdict and apply the appropriate remediation.
4. Does this change what end users see or do?
No. Employees keep the same inbox and notification experience they already have. The integration is entirely on the admin and investigation side.
5. What do I need to use this integration?
Defender for Office 365 Plan 2 or Microsoft 365 E5 licenses, along with Proofpoint Core Email Protection deployed via API. Customers on Collaboration Security Tier 2, Tier 3, or Prime already have Core Email Protection, since it is included in each of those.
6. Is Proofpoint part of Microsoft's official ICES Vendor Ecosystem?
Yes. Proofpoint is now part of the ICES Vendor Ecosystem, which gives eligible customers a supported way to integrate participating vendors’ email security verdicts with Microsoft Defender workflows.