Insider Threat Management

Identify Emerging Risk with Insider Threat Management

Detect motive and risky behavior across endpoint, chat, AI, email, cloud, and web to accelerate investigations and prevent harm.

insider-threat-management-data-security-employee-risk

OVERVIEW

Reduce insider risk across your organization

Insider threat management helps security teams detect and understand risky behavior, investigate suspicious activity, and prevent security incidents across channels. By combining behavioral insights, user activity, data context, and adaptive controls, it empowers teams to identify insider risk earlier and respond to security incidents faster.

Act decisively to reduce risk

Focus on the users most likely to cause harm by combining motive, behavior, and data signals.

insider-threat-management-user-activity-monitoring

Accelerate investigations with evidence

Understand what happened with user story timelines, intelligent sentiment analysis, and forensic evidence.

insider-threat-management-threat-detection-risk-analysis

Protect people and privacy

Detect threats while respecting user privacy with behavior-based monitoring anonymization.

insider-threat-management-data-loss-prevention
01 04

WHY IT MATTERS

Modern insider threats evade rule-based detection

Your users have access to sensitive data in more places than ever, from endpoints and cloud apps to email, web, and GenAI tools. And because insiders often have legitimate access, risky behavior can look like normal work until data is stolen, exposed, or misused. Security teams need visibility into user activity and motives so they can detect insider risk early and respond before damage occurs.

58 %
of orgs cite careless users and third parties as leading causes of data loss
48 %
of orgs say visibility into risky behavior is a top data security challenge
76 %
of data loss events are caused by just 1% of users
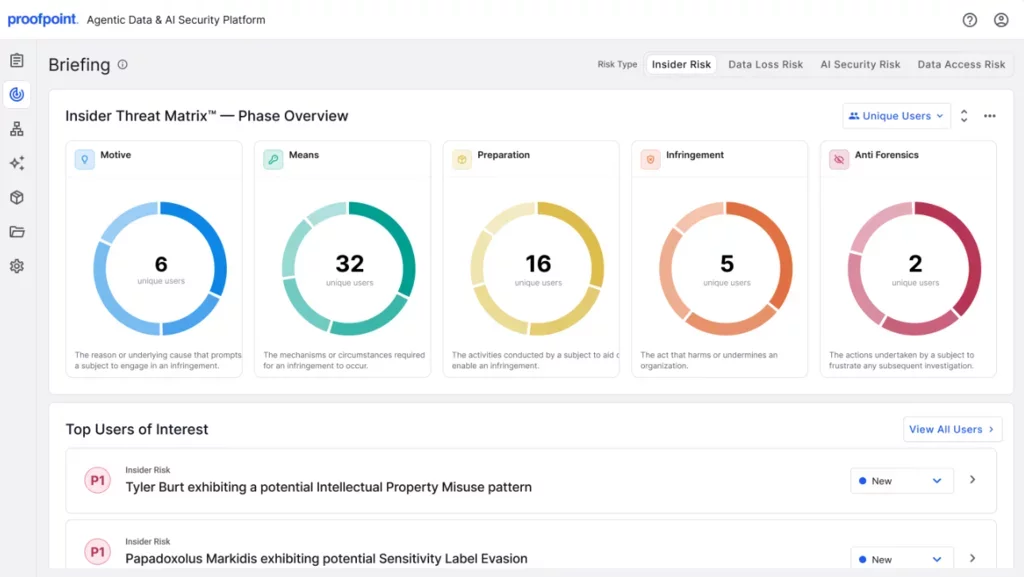
proofpoint insider threat management solutions displaying the threat matrix dashboard

PRODUCT DETAILS

See risks earlier with the team you have

Proofpoint Insider Threat Management solutions identifies high-risk users by combining behavioral insights, user activity, data movement, and human risk signals across endpoints, browsers, cloud, email, and web channels. Real-time adaptive risk monitoring helps security teams focus on the activity most likely to lead to security incidents.

User Activity Monitoring

Instantly see user behavior and activity in real time across endpoints, browsers, cloud, and email without an alert queue.

Sentiment Analysis

Understand motive by analyzing workplace communications for early risk signals.

Prebuilt Risk Detections

Start fast with out-of-the-box alert libraries, prebuilt insider threat scenarios, and customizable detection rules.

Adaptive Risk Monitoring

Elevate monitoring when users take risky actions. Combine behavior, identity, data, and motive to prevent harm.

01 04

Investigate insider incidents with full context

Bring user activity, behavioral context, and forensic evidence into a unified investigation workflow. Security teams can validate insider risk faster, understand user sentiment more clearly, and share actionable evidence with HR, legal, and compliance stakeholders during incident response.

Timeline-Based Investigations

View activity before, during, and after insider incidents in a unified investigation workflow.

Forensic Evidence Collection

Capture screenshots and activity context to validate careless or malicious behavior.

Investigation Evidence Sharing

Share forensic evidence and investigation context with your HR, legal, and compliance teams.

Privacy-by-Design Controls

Protect your users' privacy with data anonymization, masking, and role-based access controls.

01 04

Mitigate insider risk with adaptive controls

Use adaptive controls and dynamic policies to prevent risky data movement across endpoints, cloud apps, web activity, and GenAI tools. Security teams can block high-risk actions, apply policy-based protections, and guide users with in-the-moment coaching without disrupting productivity.

Real-Time Data Protection

Block risky transfers involving USB devices, cloud sync apps, web uploads, and GenAI tools.

Dynamic Policy Enforcement

Adjust controls automatically based on user behavior and insider risk indicators.

In-the-Moment Coaching

Help users learn safe data handling and rethink risky actions with customizable notifications.

Flexible Ecosystem Integration

Integrate with SIEM and SOAR workflows through APIs and webhooks.

01 04

Augment your ITM program

Strengthen your ITM program with expert guidance, operational support, and insights that help your team reduce risk faster.

Learn more about Advisory Services

WHY ORGANIZATIONS CHOOSE PROOFPOINT

Proofpoint ITM vs. static insider threat monitoring

CapabilityStatic Insider Threat MonitoringProofpoint ITM
Adaptive monitoring Requires manual policy updates as user risk changes Adjusts monitoring in real time based on user behavior and risk signals
Behavioral context Reviews individual events with limited behavioral context Combines behavior, communications, and data activity to reveal user sentiment
Cross-channel visibility Provides visibility across fewer activity sources Unifies insights across email, cloud, web, endpoints, and data movement
Human risk prioritization Prioritizes alerts rather than correlated human risk Prioritizes users by combining behavior, identity, data, and motive
Investigation context Requires investigators to piece together evidence across events Combines timelines, forensic evidence, and activity context to speed investigations
Privacy-by-design Relies on administrative controls to manage investigator access Protects privacy with anonymization, data masking, and role-based access
Adaptive data protection Applies static controls that do not auto-adjust to changing risk Applies dynamic policies, real-time controls, and user coaching to help prevent data loss

Extend data security across your organization

Combine ITM with Enterprise DLP, Adaptive Email DLP, and Email DLP and Encryption to identify risky users, protect sensitive data, and accelerate investigations.

Explore Unified Data Security

Request a Demo

Get ahead of insider threats

Detect risky behavior earlier, accelerate investigations, and reduce insider risk without slowing down your team. Request a demo and see insider threat management in action.

Frequently Asked Questions

Traditional security tools struggle to detect insider threats because they tend to rely on static rules and isolated alerts. Many risky actions look like normal activity from users with legitimate access to sensitive data. Modern insider threat management adds behavior and data context, helping security teams spot suspicious activity earlier and respond before it leads to data loss or security incidents.

Organizations should look for insider threat management (ITM) solutions that can identify risky behavior before it leads to security incidents. Many traditional security tools rely on static rules and isolated alerts, which can miss insider risk tied to normal-looking activity. Strong ITM solutions combine behavioral insights, data context, and adaptive monitoring to help security teams investigate incidents faster and focus on the biggest sources of real risk.

Insider threat management (ITM) helps security teams detect risky behavior before it leads to data breaches or data leaks. Many insider threats look like normal user activity, which makes them hard to detect with static rules alone. Modern ITM combines behavioral insights, adaptive controls, and real-time monitoring to help protect confidential information and reduce insider risk.

Insider threat management focuses on detecting and responding to risky activity that could lead to data loss, security incidents, or unauthorized access. Insider risk management is a broader approach that includes identifying and reducing human risk before incidents occur. Modern insider threat management solutions often combine both approaches by using behavioral insights, adaptive monitoring, and real-time controls to help security teams identify and mitigate insider risk earlier.